Risk Management
Risk Management Organization
A company’s risk management capabilities play a critical role in addressing risks and opportunities arising from both internal and external factors. Global trends and environmental changes may significantly impact a company’s profitability and even its long-term survival.
Risk Management Organization
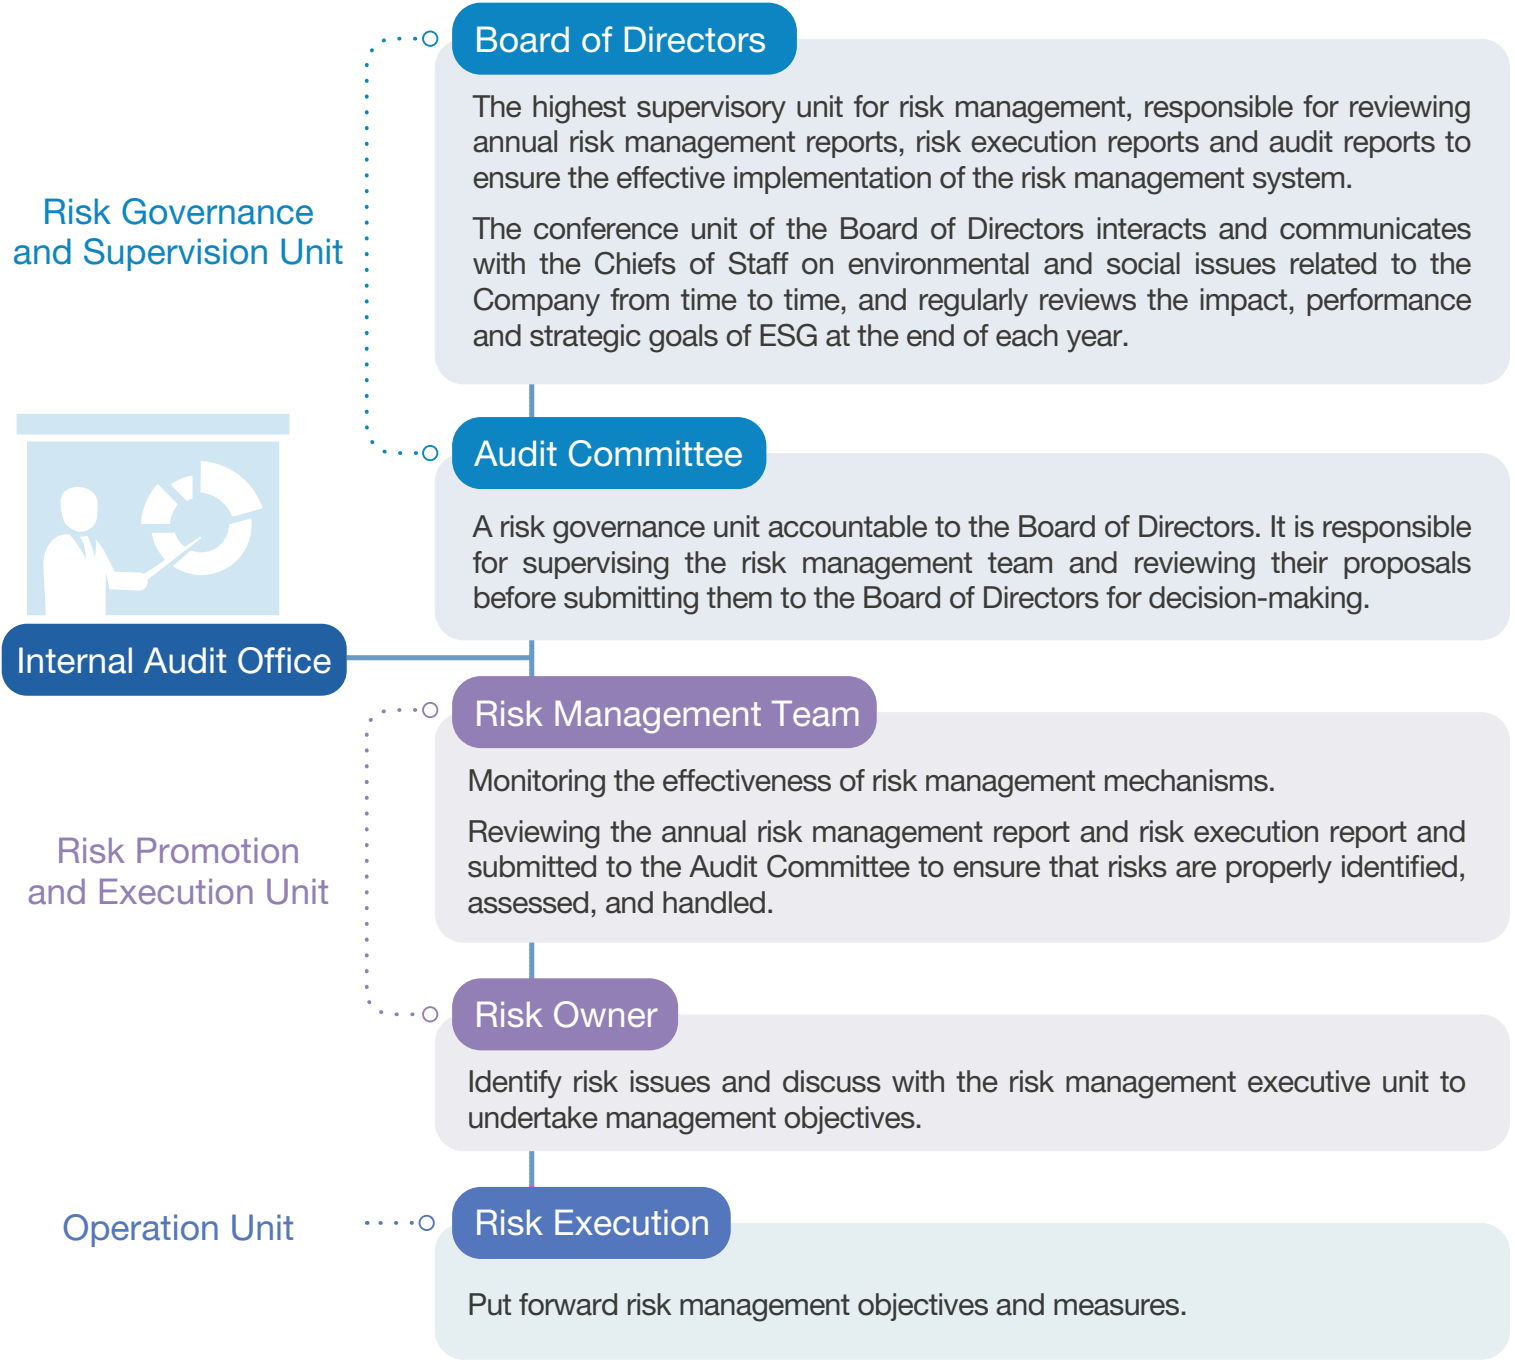
Construct a proactive risk management mechanism so that relevant units can respond to risk events in a timely manner through risk management procedures, reduce or avoid the impact of risk events, and ensure sustainable operations.
The responsibilities of each role are as follows:
Risk Management Policy and Process
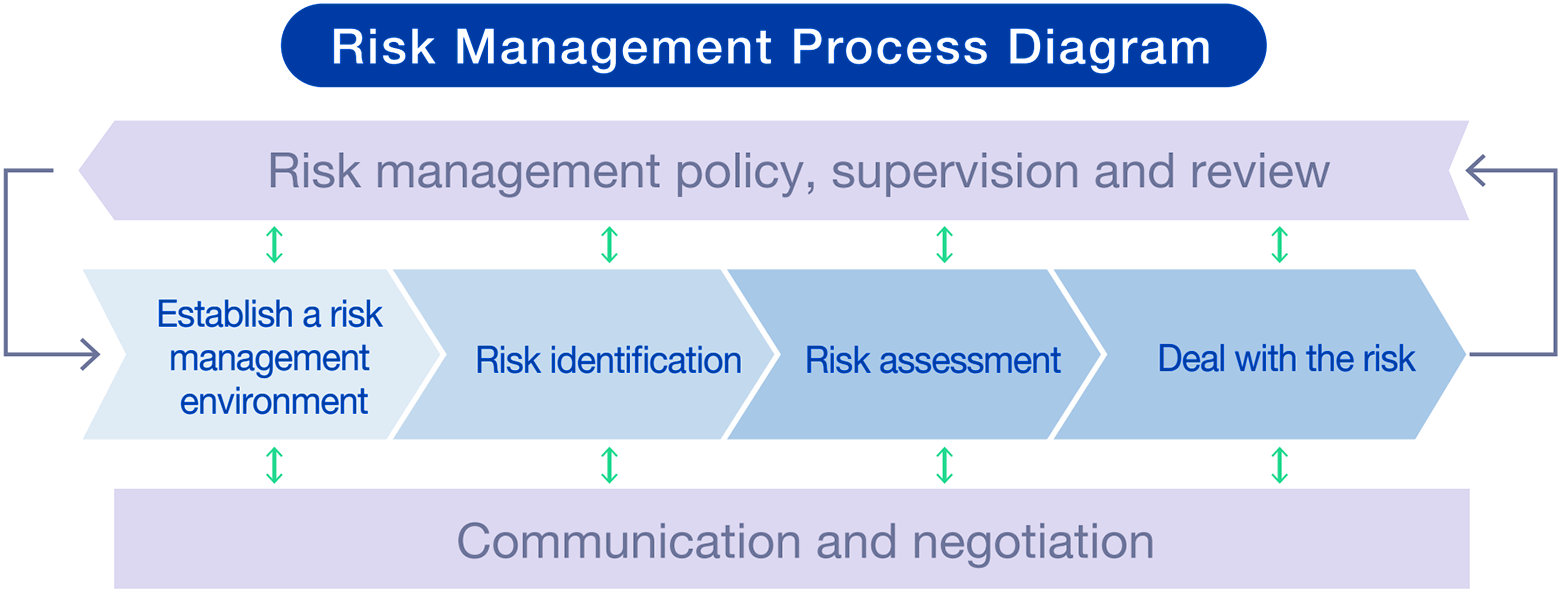
In order to strengthen corporate governance and risk control capabilities, and continue to optimize risk management policies and procedures, the company has formulated the “Risk Management Policy and Procedure” and approved by Audit Committee and the Board of Directors to determine the group’s material risk items from top-down.
The Material Risk will coordinate and control by Risk Owner, set up key risk indicators (KRI) to provide early warning functions, so that the Company can respond to and resolve the possible impacts of risks early. The risk execution unit conducts self-risk identification, analyzes the level of risk impact, and proposes a risk treatment improvement plan.
In response to possible risks that may arise in the course of business both internally and externally in a systematic way and in line with annual plans. We have developed the “Risk Management Operation Manual" to ensure the effective implementation of risk management operations. For material incidents, in order to immediately reduce disasters and resume normal operations, we also set up the “Crisis Management Operation Process.”
 Risk Management Policy and Procedure
Risk Management Evaluation Matrix
We conduct risk and opportunity matrix analysis to identify the possibility and the influence degree, and each give them a score of 1 to 3. The probability multiplied by the influence degree will become the risk level, and then take corresponding actions.
Explanation of Risk Evaluation Matrix
Other Related Information
In the changing environment, new types of risks are constantly emerging, including climate crises, sudden disease crises, and the like, which have a huge impact on the environment, society, and economy. At the same time, companies must continue to review and adjust response strategies to remain competitive.
For climate change risk management and response, please refer to "Climate Change Risks and Opportunities"
For the assessment of other opportunities and risks, please refer to Opportunities and Risks
Internal Audit System
Independence
The internal audit unit (Auditor Office) is subordinate to the Board of Directors, and set up an Audit Supervisor. The appointment, removal, evaluation and remuneration of the Audit Supervisor shall be approved by the Audit Committee and Remuneration Committee before a resolution of the Board of Directors. In addition, the appointment, removal, evaluation and remuneration of other auditor staffs, should be reported by the Audit Supervisor, and approved by the Chairman of the Board of Directors. Audit supervisors are required to attend all Audit Committee and Board meetings and report on the implementation of internal audit business. Communication meetings are arranged twice a year with Independent Directors.
Risk orientation
Formulate and implement the Group's annual audit plan based on the risk assessment results, and plan audit operations based on the risk assessment results and control status of the audit items.
Professional ability
The audit team holds certifications such as Certified Internal Auditor (CIA) and Certified Information Systems Auditor (CISA). They exceed annual continuing education requirements and engage professional assistance as needed for business demands. The internal personnel are certified as International Sustainability Disclosure Professional and as ISO 9001 auditors, collaborate with external consultants in third-party verification processes, and provide improvement recommendations.
The internal audit organization, operation, and process
Digital Resilience and Information Security
Information security risks, such as ransomware attacks, social engineering, and data breaches, continue to be regarded by experts and decision-makers worldwide as one of the most critical operational risks. As companies advance in digital transformation, the scope of cybersecurity threats continues to expand. The rise of emerging technologies, including artificial intelligence (AI), further increases the challenges of risk management. In the face of escalating cybersecurity risks, “digital resilience” has become a key capability for enterprises to maintain stable operations and respond effectively to unexpected security incidents.
As a real estate brokerage, Sinyi Realty relies heavily on large databases and information systems to serve clients. During property transactions, the Company also handles extensive customer data. Therefore, the stable operation of its information systems and the safeguarding of information security are not only essential for business continuity but also a significant competitive advantage. Enhancing digital resilience and cybersecurity is fundamental to ensuring continuous operations, while also driving sustainable management and strengthening stakeholder trust.
Within Sinyi Group, the IT Service & Information Security Management Department is responsible for setting internal information security policies, planning and implementing security operations, and promoting the enforcement and continuous improvement of cybersecurity measures. To ensure the effectiveness of the management framework, the department regularly reports on the implementation progress and outcomes of the information security program to the Board of Directors each year, thereby enhancing the overall level of cybersecurity governance within the organization.
Information security management policies and measures